Automatic Threat Containment
Put a stop to suspicious activity, including AI-powered threats.




Stop Threats and Eliminate Disruption Risk
Cyber threats are a top concern for any business, and for most, antivirus and occasional security scanning is not enough to protect against ransomware attacks.
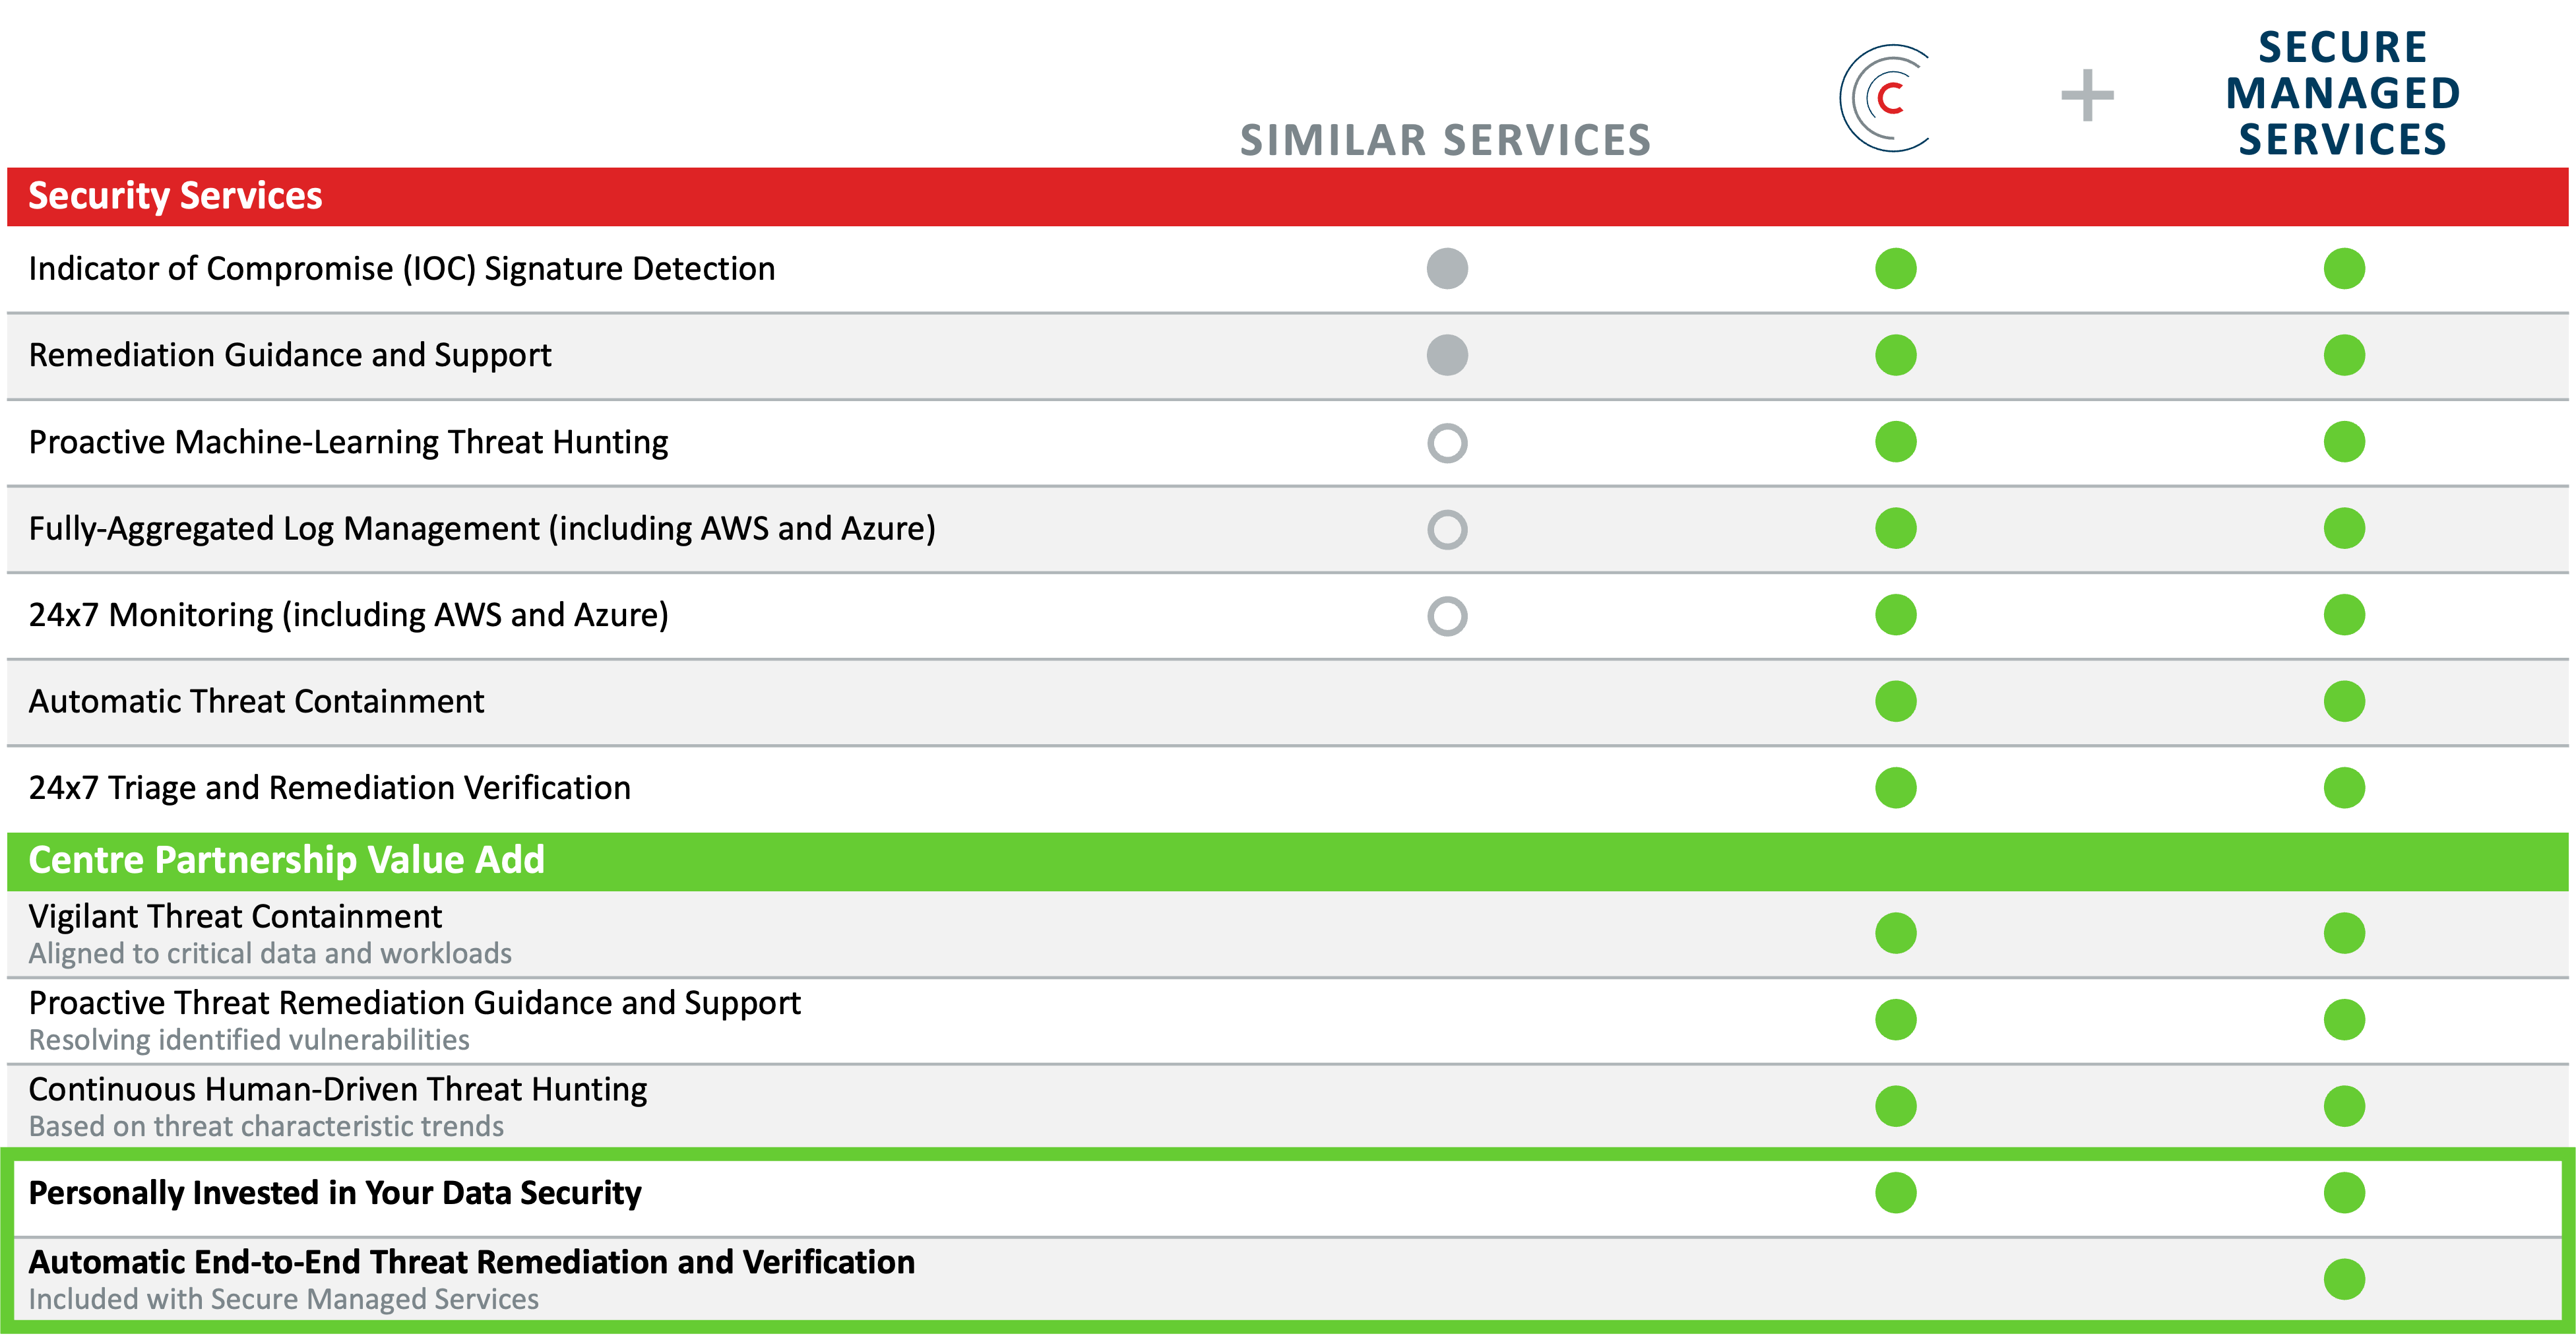
AI-enhanced analysis identifies suspicious behavior and reduces alert noise faster, while Centre's security and AI experts validate activity and guide containment, recovery, and remediation.
As your front line of defense, Managed Detection and Response (MDR) goes beyond alerts and automatically stops threats, in real time.
At Centre, we provide the entire package, backed by proven processes and a Security Operations Centre (SOC). We manage alerts, contain malicious traffic before they can do damage and guide you through recovery and remediation.
Still have questions? We're here to help.

Prevent Threats from Spreading
Stop threats, including AI-powered, in their tracks with 24x7 monitoring.
Avoid Severe Damage
Resolve vulnerabilities fast with threat remediation guidance and support.
Transparent Incident Response
Security summary that include incident details and long-term recommendations.
Automatic Threat Remediation and Verification
Automatically removes risks and adjusts IT strategy based on scanning results. Included with Secure Managed Services!


Managed Detection and Response Enhanced with AI
AI added for smarter and faster Automatic Threat Containment.
-
Faster Threat Detection and Response
Identifying and escalating threats quickly to reduce response time and limit potential damage.
-
Reduced Noise with High-Confidence Alerts
Filtering events to remove false positives and surface only useful alerts.
-
Improved Accuracy in Threat Detection
Using behavioral-based analytics to spot real threats earlier and reduce overall risk.
-
Increased Insight into Security Activities
Providing consolidated insight into log activity for better awareness and control.
-
Lower Cost from Better Efficiency
Reducing the need for multiple SOC analysts by automating analysis and grouping.
Real-Time Threat Detection
with Dedicated SOC Support
Get more with a single solution that protects your employees, data, and devices. Plus, a team of cybersecurity experts personally invested in your data security.
What makes our Managed Detection and Response services better


Incident Response
(IR)
Recover quickly from cyberattacks and breaches, from threat containment to business restoration

Cloud Detection
+ Response (CDR)
24x7 monitoring and containment across your entire cloud ecosystem, including hosted virtual machines, Microsoft 365, Azure, AWS, and Google Cloud

Endpoint Detection
+ Response (EDR)
Endpoint isolation capabilities that prevent security threats and suspicious activity from accessing other networks and devices

Comprehensive Log Management (SIEM)
Not sure which cybersecurity solution is best for you?
We're here to help!


Personalized
Service
We get to know your business and people for a true partnership that fits how your business actually works

Local
Touch
Familiar faces in your community, staying engaged and working alongside you through every technology challenge

Enterprise
Experience
People, processes, and AI-enhanced technology that adapt to evolving cybersecurity and IT demands
Frequently Asked Questions About Managed Detection and Response Services
How does Centre Technologies handle threat detection and response?
Centre Technologies goes beyond basic alerts by automatically stopping threats in real time. Their MDR service includes:
- 24x7 monitoring through a dedicated Security Operations Center (SOC).
- Automatic threat containment and remediation, preventing malicious traffic before damage occurs.
- Guidance through recovery and remediation after incidents.
What level of transparency and reporting does Centre provide customers?
Does Centre remediate detected threats and activities?
Yes. Centre delivers true incident response, not just alerts and ticket escalations. For customers with Secure Managed Services, containment and remediation of threats is automatic.
For customers without Secure Managed Services, detailed recommendations for remediating threats are provided.
What makes Managed Detection and Response services from Centre Technologies better than other managed security providers?
Enterprise experience. Personalized service. Local touch.

Insights on Managed Detection + Response
Learn more about how technology transforms and protects your organization.